
Shadow AI arises when professionals use artificial intelligence tools, models, or agents without the knowledge, authorization, or oversight of the responsible teams. Although it often serves legitimate goals of productivity and innovation, it can create risks related to sensitive information, permissions, connections to corporate systems, traceability, regulatory compliance, and costs. The solution is not to slow down the adoption of AI, but to establish governance, security, and control mechanisms that allow it to be leveraged safely.
Shadow AI is the use of artificial intelligence tools, models, or agents outside of corporate controls—a practice that can compromise data, security, compliance, traceability, and costs.
What is Shadow AI, and why does it concern cybersecurity leaders?
Shadow AI refers to the use of artificial intelligence tools, models, or agents without the visibility, authorization, or control of an organization’s technology, security, privacy, or compliance teams.
Halloween has come and gone, but some nightmares last far longer than a single night.
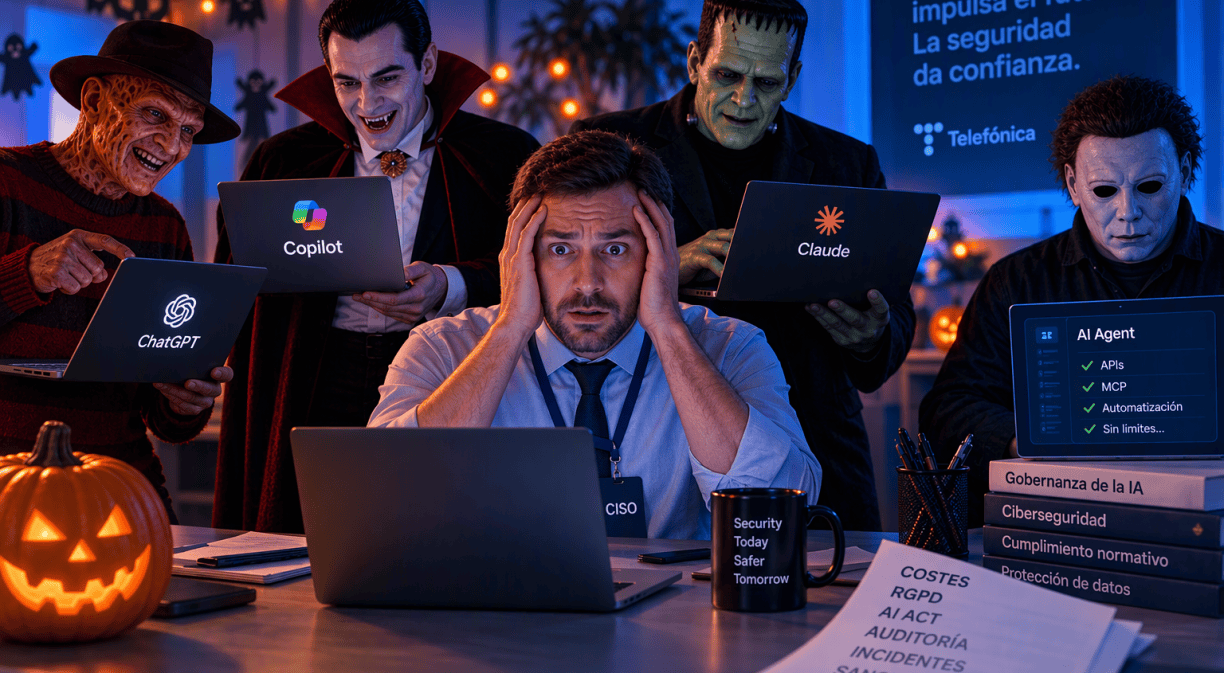
Our protagonist, Daniel, is the CISO of a software-as-a-service (SaaS) company. He was enjoying a costume party with his coworkers: music, a few drinks, and—for once—not a single security alert.
Everything was going great until Freddy Krueger approached, drink in hand.
“AI is amazing!” This morning I uploaded our customer database to a public generative AI tool, and it gave me an analysis of our portfolio in seconds—with names, phone numbers, and everything!
Our CISO nearly spit out his drink.
“Excuse me, Freddy… Where did you upload our customers’ personal data?”
What are the risks of entering corporate information into unauthorized AI tools?
Entering personal data, financial forecasts, contracts, or other corporate information into unauthorized AI tools can make it difficult to control how that data is processed, accessed, stored, and potentially exposed. The level of risk will depend on the service used, its configuration, the applicable terms and conditions, and the controls implemented by the organization.
Before he could get an answer, Dracula appeared.
“That’s nothing! I’ve entered our sales forecasts and next quarter’s margins into an AI assistant. It’s prepared a spectacular presentation for the committee for me.”
Our protagonist’s smile began to fade.
Frankenstein arrived from behind, proud of his latest creation.
“Well, I’ve connected an AI agent to our contract repository!” Now it can view documents, search for clauses, and share information automatically. I’ve given it access to everything so I don’t have to deal with permissions.
“To everything? Who authorized those connections? Do we have visibility into what that agent is doing?”
Frankenstein shrugged.
What risks do AI agents with excessive permissions pose?
An AI agent with broad permissions can access more information than necessary, interact with different systems, and perform actions without sufficient oversight. That’s why it’s important to implement access controls, limit permissions, and maintain traceability of its activity.
And then Daniel saw Michael Myers. He was sitting in a corner, silent, staring intently at his laptop.
“Michael… What are you doing?”
Michael slowly turned his screen toward him.
His autonomous AI agent had been chaining together calls to various application programming interfaces—known as APIs—for hours, consuming millions of tokens with no apparent limit.
Just then, the CFO appeared, also in costume, but holding a five-figure bill in his hand.
The music stopped.
How can Shadow AI affect costs and regulatory compliance?
The use of AI tools and agents without limits on consumption, oversight, or authorization criteria can lead to unexpected costs. It can also raise concerns regarding data protection, security, internal liabilities, and compliance with applicable regulations.
The head of the legal department showed up asking about the processing of personal data. The CEO wanted explanations. And someone had just announced a special audit.
General Data Protection Regulation, European Artificial Intelligence Regulation, potential security incidents, liabilities, unexpected costs…
AAAAAHHH!
Daniel woke up with a start.
He looked at the clock. Seven in the morning.
It had all been a nightmare.
Well, almost all of it.
Why does Shadow AI appear within companies?
Shadow AI almost never starts with malicious intent. It usually appears when someone tries to work faster, automate a task, analyze information, or improve their productivity using a tool that isn’t part of the authorized technology environment.
Because, even though Freddy, Dracula, Frankenstein, and Michael Myers are fictional characters, what Daniel had just experienced has a very real name: Shadow AI.
We’re talking about the use of artificial intelligence tools, models, and agents without the visibility or control of the teams responsible for technology and security.
The interesting thing is that it almost never starts with malicious intent. It begins with someone who wants to work faster, automate a task, or improve their productivity.
The problem arises when innovation moves faster than the company’s controls.
How can companies manage Shadow AI without stifling innovation?
Companies can reduce the risks of Shadow AI by gaining visibility into the tools being used, protecting sensitive information, implementing access controls, limiting permissions, monitoring connections, and tracking agent activity and usage.
The goal should not be to prevent the use of artificial intelligence, but rather to create an environment where it can be used responsibly and in alignment with the organization’s policies.
To do this, it is necessary to know which AI tools are being used, for what purpose, what information they process, and which systems they can access. The organization must also establish clear criteria for approving tools, classify the information that can be entered into them, and determine which actions require human oversight.
In the case of AI agents, it is especially important to apply the principle of least privilege: each agent should have access only to the information and functions necessary to complete its task.
It is also advisable to establish controls over APIs, connections based on the Model Context Protocol (MCP), and other integrations used to connect AI models with repositories, applications, or corporate systems.
Monitoring activity, permissions, and usage helps detect anomalous behavior, unnecessary access, and costs that exceed established limits.
What role do governance and cybersecurity play in AI adoption?
Artificial intelligence governance enables the definition of responsibilities, authorization processes, technical controls, and usage criteria. Cybersecurity helps protect information, monitor connections, and reduce exposure associated with uncontrolled tools or agents.
Leveraging its cybersecurity capabilities and in collaboration with technology partners, Telefónica supports companies in adopting artificial intelligence through measures aimed at:
- Gaining visibility into the AI tools being used.
- Protecting sensitive information.
- Establishing controls over APIs, MCP connections, and other integrations.
- Limiting the permissions assigned to AI agents.
- Monitoring activity and usage.
- Defining governance and compliance policies tailored to the organization.
This approach connects innovation with trust and facilitates access to advanced digital technologies without compromising security, accountability, and control.
Because the goal is not to slow down innovation, but to prevent the next Halloween nightmare from becoming a real-life incident.
Frequently Asked Question
What does “Shadow AI” mean?
Shadow AI refers to the use of artificial intelligence tools, models, or agents without the visibility, authorization, or control of an organization’s technology, security, privacy, or compliance teams.
Why do employees use unauthorized AI tools?
Typically, they’re looking to work faster, automate tasks, analyze information, or improve their productivity. The problem arises when they use these tools outside the controls established by the company.
What information should not be entered into an unauthorized AI tool?
The article identifies personal data, sales forecasts, financial margins, contracts, and other corporate documents as particularly sensitive information. Its use will depend on internal policies, the tool, its configuration, and the applicable conditions.
What risks can an AI agent with access to corporate systems pose?
It can access unnecessary information, share content, establish connections with different systems, consume resources without limits, or perform actions without sufficient oversight and traceability.
How can Shadow AI be controlled?
Through visibility into the tools used, protection of sensitive information, authorization criteria, controls over APIs and integrations, limited permissions, activity monitoring, and governance policies.
Does controlling Shadow AI mean preventing the use of artificial intelligence?
No. The goal is to enable the organization to take advantage of